OpenClaw Explained: The Self-Hosted AI Agent That Executes on Your Systems
Most AI tools today just answer questions - OpenClaw actually does the work. This powerful self-hosted agent can execute commands, modify files, and automate tasks directly on your systems. But with great power comes great responsibility - learn how to adopt OpenClaw safely with proper governance controls.
What Is OpenClaw?
OpenClaw represents a fundamental shift in how businesses can leverage AI. Unlike conversational chatbots that merely provide information, OpenClaw is an execution agent that performs real work on systems you control. It runs persistently on your machines - whether laptops, virtual machines, or servers - and can execute tasks ranging from file operations to API calls.
The key innovation is persistence. While most AI systems treat each interaction as a fresh start, OpenClaw maintains context across sessions. This enables it to chain tasks over time, remember previous decisions, and avoid repeating setup work. In practice, this transforms AI from an advisory tool into a reliable operator for repeatable work.
Core capability: OpenClaw crosses the boundary from providing advice to executing actions. If you ask it to find files, extract insights, and save a summary, it doesn't just describe the steps - it performs them on the machine where it's running.
Key Differences From Other AI Systems
Understanding where OpenClaw fits in the AI landscape is crucial for safe adoption. Traditional chatbots are low-risk because they primarily produce text. Retrieval-Augmented (RA) systems add document access, creating moderate risk. OpenClaw introduces execution capabilities, placing it in the high-risk category.
Risk spectrum: Chatbots (low risk) → RA systems (moderate risk) → OpenClaw (high risk). Each serves different purposes and requires appropriate governance.
This distinction creates both opportunities and responsibilities. OpenClaw can automate developer onboarding, perform DevOps housekeeping, and orchestrate internal tools - tasks that previously required manual intervention or brittle scripts. But this power demands careful permission management and logging.
OpenClaw Architecture Explained
OpenClaw's architecture is designed for operational reliability while maintaining security boundaries. The system consists of five key layers that work together to transform human intent into executed actions.
Layer 1: Persistence
Unlike stateless chat systems, OpenClaw maintains long-term context through local markdown files. This persistence enables task chaining across days and consistent operation without repetitive setup.
Layer 2: Gateway
Humans interact with OpenClaw through Slack, Discord, or command line interfaces. This layer handles authentication, message routing, and response formatting - making it a critical security surface.
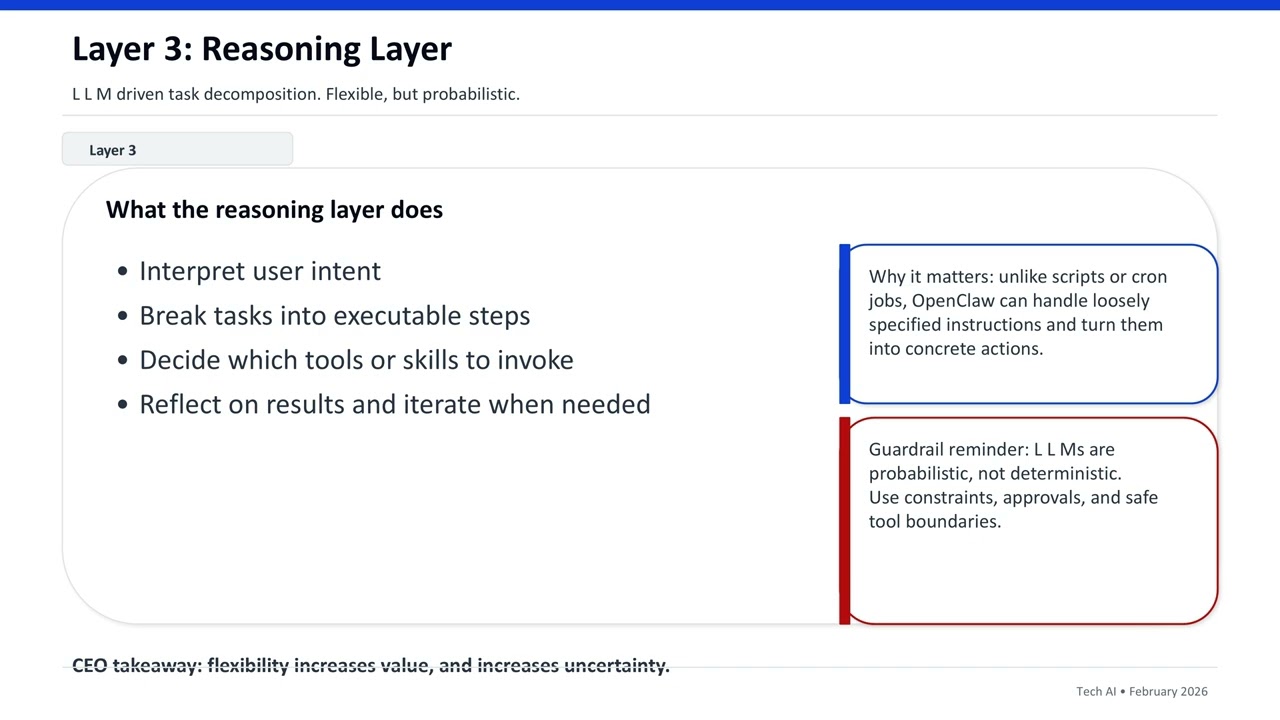
Layer 3: Reasoning
An LLM interprets intent, breaks work into steps, selects appropriate skills, and verifies results. While powerful, this probabilistic layer requires guardrails to prevent unpredictable behavior.
Layers 4 & 5: Execution
The skills layer (file operations, shell commands, APIs) and memory layer (context storage) are where work becomes real. These layers represent the security boundary between AI and your systems.
Design choice: OpenClaw is intentionally headless - it works through commands and APIs rather than UI automation. This improves reliability but reduces visibility, requiring compensatory logging.
Security Risks and Governance
The phrase "shadow super user" captures OpenClaw's risk profile. It inherits all permissions of the account under which it runs - meaning an agent with root access effectively has full system control.
Key risks include:
- Prompt injection escalating to command execution
- Gateway misconfigurations creating remote control channels
- Inadequate logging obscuring operational changes
Successful deployments implement:
- Least privilege access models
- Action allow-lists (not deny-lists)
- Comprehensive audit trails
- Human approval workflows for sensitive actions
Critical insight: The differentiator in successful OpenClaw deployments isn't model intelligence - it's governance. Organizations must treat corrections like change management, updating instructions and validating behavior over time.
Practical Use Cases
OpenClaw shines in scenarios where intent needs translation into repeatable action. These high-leverage applications demonstrate its operational value:
Developer Onboarding
Replace brittle checklists with conversational guidance while OpenClaw executes setup steps consistently across all new hires.
DevOps Housekeeping
Delegate log rotation, disk cleanup, updates, and backup verification with automated summaries and logs.
Incident Triage
Gather evidence quickly during outages while following strict playbooks for remediation.
Internal Tool Orchestration
Connect command-line tools and move data between systems without custom scripting.
Pattern: In each case, OpenClaw turns human intent into reliable, logged execution - particularly valuable for repetitive operational tasks where mistakes are costly.
Implementation Framework
Adopting OpenClaw successfully requires matching technical capability with organizational readiness. Follow this maturity path:
Technical Prerequisites
- Basic shell literacy
- Secure deployment practices
- Strong observability infrastructure
Organizational Requirements
- Governance approvals
- Centralized logging
- Security partnership from day one
Decision framework:
- Early stage: Learn in a sandbox with dummy data
- Strong DevSecOps: Build custom implementations
- Lower risk tolerance: Consider commercial alternatives
Deployment truth: When implementations fail, it's rarely the technology - it's skipping basics like clear scope, least privilege, and change management.
Watch the Full Tutorial
See OpenClaw in action with this detailed walkthrough of its architecture and capabilities. At 4:32 in the video, you'll see a live demo of OpenClaw automating a developer onboarding workflow.
Key Takeaways
OpenClaw represents a fundamental shift from advisory AI to operational AI. This transition creates real leverage but demands discipline in implementation and governance.
In summary: Start with sandbox pilots, implement least privilege access, maintain comprehensive logging, and focus on measurable value. Successful OpenClaw deployments treat the agent like a privileged service account - with appropriate rules, logs, and approvals.
Frequently Asked Questions
Common questions about OpenClaw
While ChatGPT provides conversational responses, OpenClaw executes actions on your systems. It can run shell commands, modify files, call APIs, and perform other operational tasks directly on machines you control.
This makes it fundamentally different from purely advisory AI systems. OpenClaw isn't just answering questions - it's performing the work you would otherwise do manually.
- ChatGPT: Answers questions about work
- OpenClaw: Actually does the work
- Key distinction: Execution capability vs. information retrieval
The primary risks come from OpenClaw's ability to execute commands with the permissions of its host account. Without proper governance, this could lead to accidental or malicious system changes.
Key risks include prompt injection attacks, privilege escalation, and unintended file modifications. The agent essentially becomes a "shadow super user" with whatever access rights its host account possesses.
- Prompt injection leading to command execution
- Gateway misconfigurations creating attack surfaces
- Inadequate logging obscuring operational changes
Start with a sandbox environment containing dummy data. This allows you to test OpenClaw's capabilities without risking production systems.
Once you've established proper governance controls and monitoring, you can gradually expand to more sensitive environments. Always begin with least privilege access and expand permissions cautiously.
- Initial deployment: Isolated sandbox with test data
- Second phase: Non-critical systems with limited permissions
- Production: Only after establishing strong controls
Common use cases include developer onboarding automation, DevOps housekeeping tasks, incident triage assistance, internal tool orchestration, and personal workflow automation.
These applications benefit from OpenClaw's ability to execute repetitive operational tasks consistently. For example, it can automate new developer environment setup while providing conversational guidance throughout the process.
- Developer onboarding workflows
- DevOps maintenance tasks (log rotation, cleanup)
- Incident response evidence gathering
OpenClaw uses local markdown files to store long-term context, including task summaries and action logs. This persistence enables it to remember decisions and avoid repeating setup steps.
Unlike stateless chat systems, OpenClaw maintains continuity between sessions. This allows it to chain tasks over time and build upon previous work rather than starting fresh with each interaction.
- Context stored in local markdown files
- Task summaries and action logs maintained
- Enables multi-session workflows
Implementing OpenClaw requires basic shell literacy, secure deployment practices, and strong observability capabilities. Teams should understand system permissions and logging requirements.
Before deploying OpenClaw in production, organizations need expertise in access control models, change management processes, and operational monitoring. These skills are more critical than specific programming knowledge.
- Basic command line proficiency
- Understanding of system permissions
- Ability to implement comprehensive logging
Unlike RPA tools that automate UI interactions, OpenClaw works through commands, APIs, and files. This makes it more reliable for server-side automation but requires different monitoring approaches.
While RPA tools simulate user actions, OpenClaw operates at the system level. This distinction affects both capability and risk profile, with OpenClaw typically offering more power but requiring stronger governance.
- RPA: UI automation, visual monitoring
- OpenClaw: System-level operations, log-based monitoring
- Different risk profiles and use cases
GrowwStacks helps businesses safely implement AI agents like OpenClaw with proper governance controls. We design secure deployment architectures and implement least privilege access models.
Our team identifies high-value use cases, implements sandbox environments, and establishes monitoring systems to ensure operational AI delivers value safely. We help you gradually expand to production systems with appropriate safeguards.
- Free consultation to assess your automation readiness
- Secure deployment architecture design
- Governance model implementation
- Gradual production rollout support
Ready to Implement Operational AI Safely?
Every day without automation means lost productivity and manual errors. GrowwStacks helps businesses implement OpenClaw and other AI agents with proper governance controls from day one.