The Problem
Implementing secure Single Sign-On (SSO) with SingPass requires a reliable mechanism for distributing public keys used to verify JSON Web Tokens (JWTs). Manually managing and serving these keys is time-consuming and prone to errors. Developers needed a way to automate this process to ensure high availability and security.
Without an automated solution, organizations faced challenges in keeping keys up-to-date, responding to key rotation requirements, and maintaining a secure endpoint. This often led to authentication failures, security vulnerabilities, and increased operational overhead.
The Solution
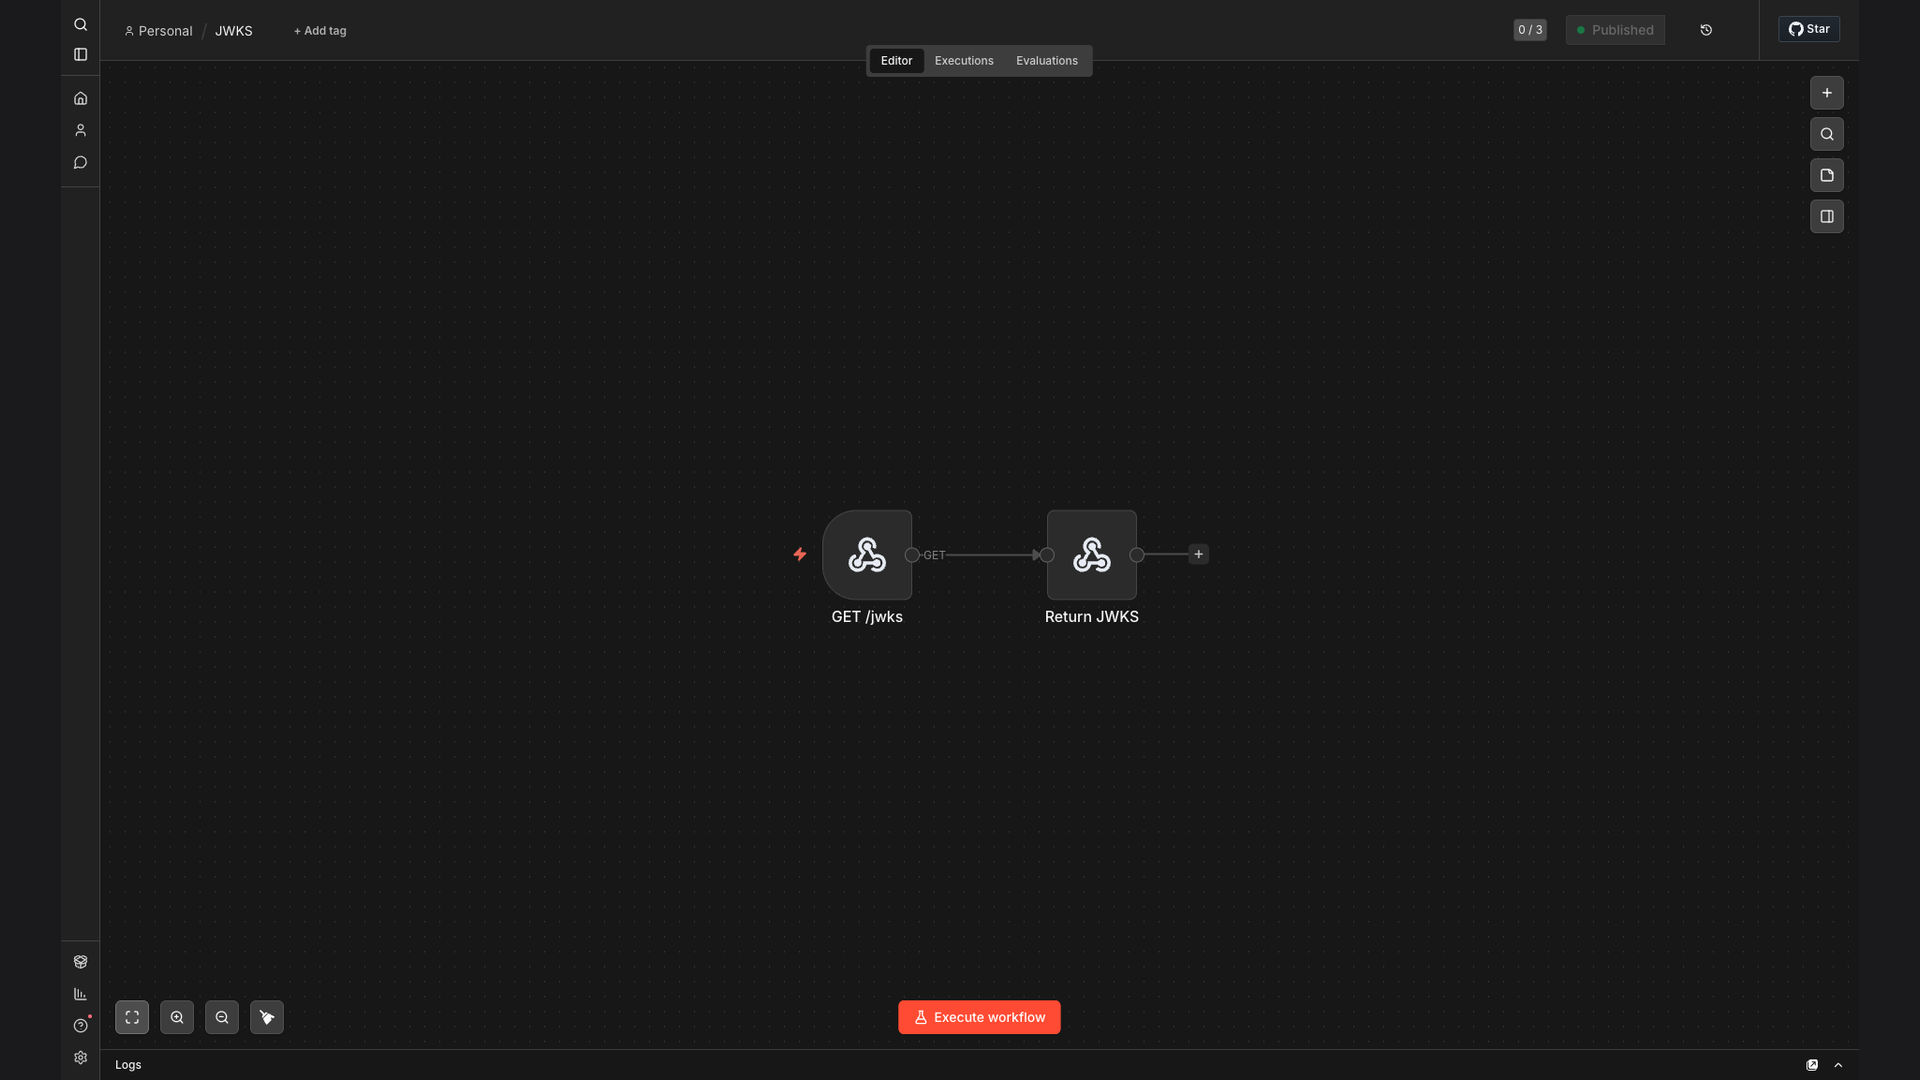
We built an n8n workflow that automates the serving of a JWKS (JSON Web Key Set) endpoint. This workflow retrieves the latest public keys, formats them into the required JWKS format, and exposes them via an HTTP endpoint. This ensures that the keys are always up-to-date and readily available for SingPass authentication.
n8n was chosen for its flexibility, scalability, and ability to handle complex workflows. Its webhook and API integration capabilities made it ideal for creating a secure and reliable JWKS endpoint. The workflow also includes error handling and monitoring to ensure high availability.
How It Works — Automated Key Distribution
The n8n workflow automates the entire process of serving a JWKS endpoint, ensuring that the public keys are always up-to-date and readily available for SingPass authentication.
- Retrieve Public Keys: The workflow starts by fetching the latest public keys from a secure source, such as a key management system or a secure API.
- Transform to JWKS Format: The retrieved keys are then transformed into the required JWKS (JSON Web Key Set) format, which includes the necessary metadata for each key.
- Create HTTP Endpoint: An HTTP endpoint is created using n8n's webhook functionality, which will serve the JWKS data.
- Set Response Headers: The appropriate response headers are set to ensure that the JWKS data is served correctly and securely.
- Serve JWKS Data: The JWKS data is served via the HTTP endpoint, making it accessible to systems that need to verify JWTs.
- Implement Error Handling: Error handling is implemented to catch any issues that may arise during the process, such as key retrieval failures or formatting errors.
- Monitor Endpoint: The endpoint is monitored to ensure high availability and to detect any suspicious activity or unauthorized access attempts.
- Automate Key Rotation: The workflow can be configured to automatically rotate the keys on a regular basis, further enhancing security.
💡 Security Best Practices: Secure key storage, HTTPS, access control, key rotation, and monitoring are crucial for implementing a secure JWKS endpoint.
What This System Does That Manual Process Can't
Enhanced Security
Automated key rotation and secure key management reduce the risk of using compromised or outdated keys.
Time Savings
Eliminates the need for manual key distribution and management, saving significant time and resources.
Improved Scalability
Provides a scalable solution for serving public keys, ensuring that the authentication process is not disrupted during peak usage.
Reduced Errors
Automates the process of formatting and serving the keys, minimizing the risk of human errors and inconsistencies.
Simplified Management
Centralizes key management and simplifies the process of updating and distributing public keys.
Real-time Monitoring
Provides real-time monitoring of the JWKS endpoint, allowing for quick detection and resolution of any issues.
Before vs. After: Automated Key Management
Before: Manual key distribution took 2-3 hours per key rotation, with a high risk of errors and inconsistencies.
After: Automated key distribution takes less than 60 seconds, with near-zero risk of errors and improved security.
Implementation: Live in 3 Weeks
- Planning and Design: We started by understanding the client's specific requirements and designing the workflow architecture. This included identifying the secure source for public keys and defining the required JWKS format.
- Workflow Development: The n8n workflow was developed and configured to retrieve the latest public keys, transform them into the JWKS format, and expose them via an HTTP endpoint.
- Security Implementation: Security measures were implemented to ensure that the JWKS endpoint was secure and protected against unauthorized access. This included setting up HTTPS, implementing access control, and configuring key rotation.
- Testing and Validation: The workflow was thoroughly tested and validated to ensure that it was functioning correctly and securely. This included testing the key retrieval process, the JWKS formatting, and the HTTP endpoint.
- Deployment and Monitoring: The workflow was deployed to a production environment and configured for continuous monitoring. This ensures that the JWKS endpoint remains available and secure.
The Right Fit — and When It Isn't
This solution is ideal for organizations that need to implement secure Single Sign-On (SSO) with SingPass and require a reliable mechanism for distributing public keys. It is also a good fit for organizations that want to automate key management and reduce operational overhead.
However, this solution may not be the right fit for organizations that do not require SingPass authentication or that have very simple key management requirements. In such cases, a manual key distribution process may be sufficient.